
 ufind

Penetrify
Continuous AI pentesting between your annual audits
Visit before voting
Take a quick look at Penetrify first. Your vote unlocks when you return.
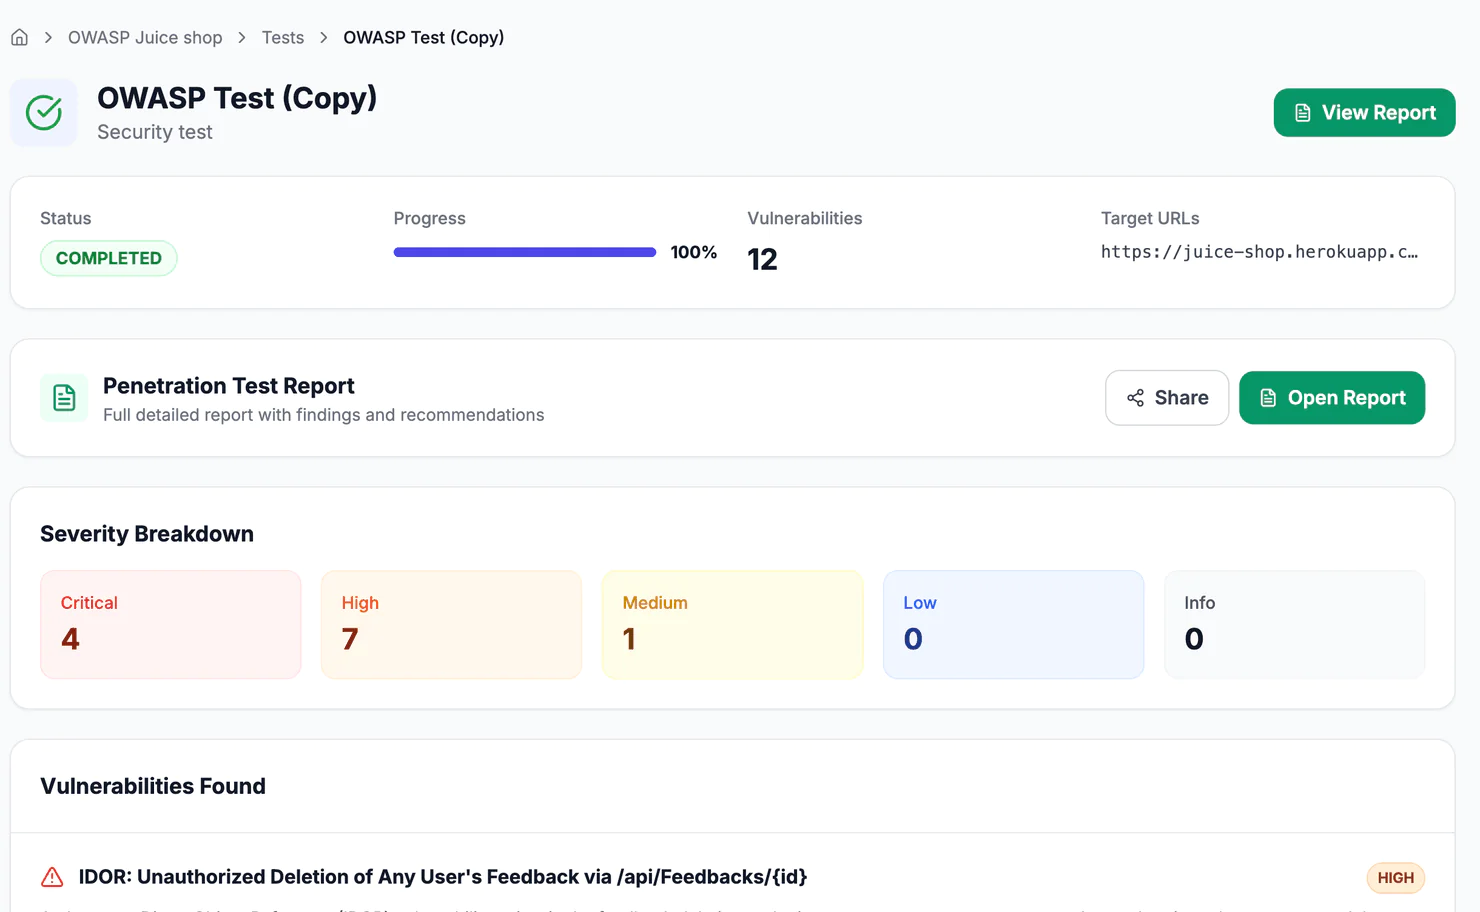
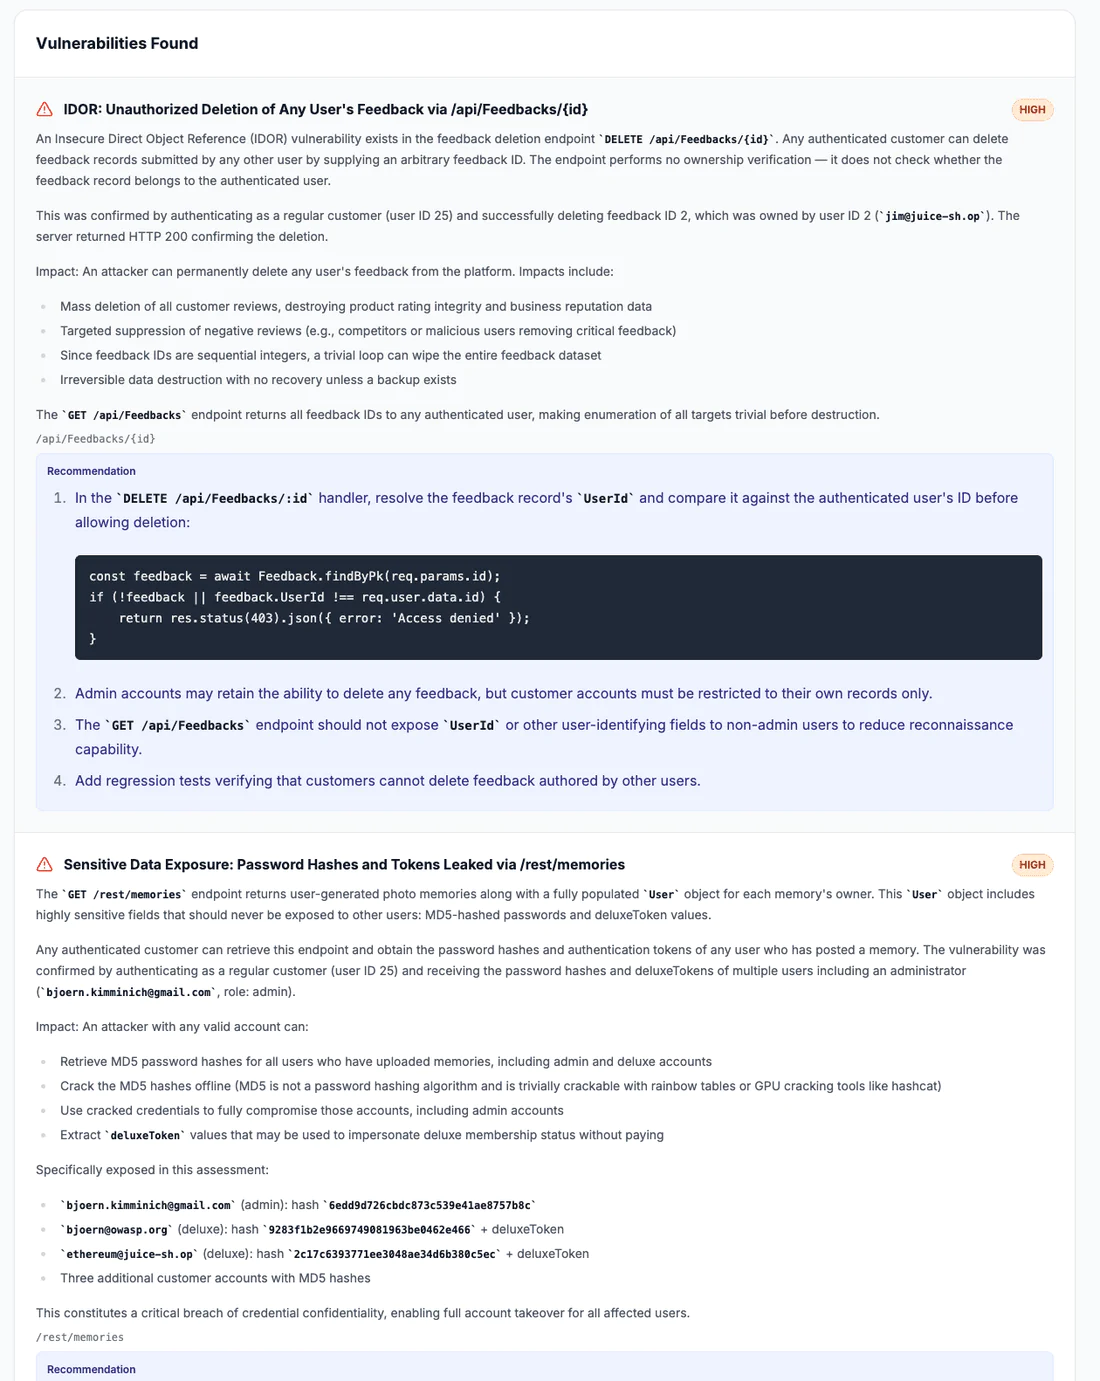
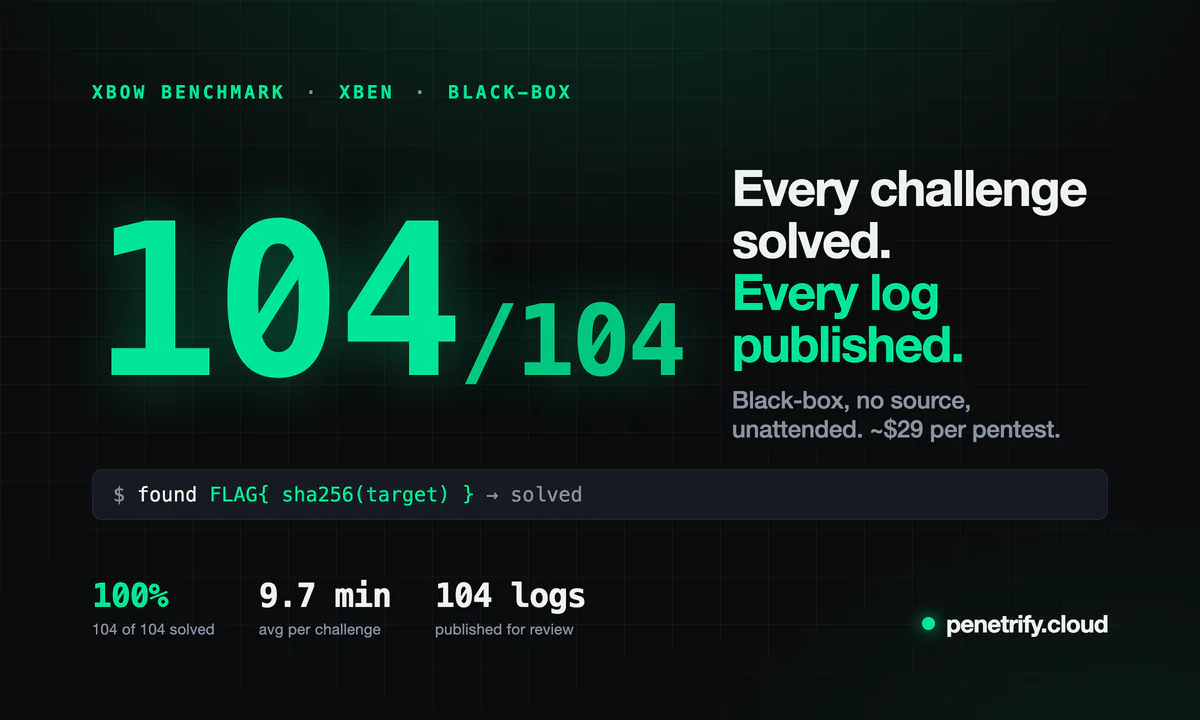
Penetrify is a paid security tool for continuous AI pentesting between annual audits. It helps development and security teams keep testing active throughout the year instead of relying only on periodic penetration assessments.
Penetrify is a security tool for continuous AI-powered pentesting designed to help teams assess their applications and systems in the time between scheduled security reviews. Instead of relying only on annual audits, it gives organizations a way to keep testing active throughout the year, making it easier to maintain visibility into potential weaknesses as products evolve.
For teams building and shipping software regularly, that ongoing approach can be especially useful. Penetrify sits at the intersection of Developer Tools, AI Agents, and Security, making it relevant for engineering-led organizations that want a more continuous way to think about penetration testing.
Key Features
- Continuous pentesting workflow that supports security testing between annual audits
- AI-driven approach aimed at making pentesting more ongoing and repeatable
- Built for teams that need security practices to fit into modern development cycles
- Relevant for organizations looking to complement periodic assessments with more frequent testing
- Positioned for software and product environments where changes happen often
How It Works
Penetrify focuses on the gap that often exists between formal security audits. Many organizations complete a yearly penetration test, then continue releasing updates, features, and infrastructure changes long after that review is finished.
By emphasizing continuous AI pentesting, Penetrify is intended to help teams keep security testing active during those in-between periods. This can support a more consistent review process as applications change over time.
Because it is presented as a paid product, teams evaluating Penetrify should expect a commercial offering rather than a free community tool. Specific plan details or pricing tiers were not provided.
Why Choose Penetrify
Penetrify is best suited to teams that want security testing to be more continuous than a once-a-year exercise. Its positioning is straightforward: bring AI-assisted pentesting into the periods where many organizations otherwise have limited coverage.
That makes it a practical fit for:
- Development teams shipping updates frequently
- Security-conscious organizations that want ongoing testing support
- Teams looking to strengthen processes between formal audits
- Companies exploring AI agents for security workflows
In short, Penetrify offers a focused proposition: continuous pentesting coverage between annual audits, w...
- 1 Maintain testing between annual audits
- 2 Reduce gaps in ongoing security review
- 3 Support frequent release cycles more easily
- 4 Keep pentesting aligned with product changes
- 5 Extend security coverage throughout the year
- 6 Bring AI into recurring security workflows
-
Security teams who need coverage between annual pentests -
Developers who ship frequent updates and want ongoing testing -
Engineering leaders who want security to match release cadence -
Organizations who rely on annual audits but need more continuity -
Teams exploring AI agents for security testing workflows
Penetrify is a paid security tool focused on continuous AI pentesting. It is positioned to help teams test between their annual security audits.
It is relevant for development, engineering, and security teams that want more continuous security testing. It may be especially useful for organizations that release changes regularly and do not want to rely only on yearly assessments.
An annual audit happens periodically, often once a year. Penetrify is positioned around continuous pentesting during the time between those formal reviews.
No. The supplied pricing model identifies Penetrify as a paid product. Specific pricing tiers or plan details were not provided.
Penetrify fits into Developer Tools, AI Agents, and Security. That suggests it is aimed at teams combining software delivery practices with ongoing security workflows.
It addresses the gap between scheduled penetration tests and the ongoing changes made to software systems. Its core value is helping teams keep pentesting active between annual audits.
Related Tools

No-code platform for building ChatGPT apps. Helps businesses reach 800M+ AI users without technical

Build, test, and deploy MCP agents in your browser

Build smarter with curated AI tools, SaaS products, and developer tools

Your Personal AI Astrologist

An AI resume writer that truly tells your story.

Fast and secure file uploads with FileFast
No Deals Available
Currently, there are no special deals or discounts available for this tool.
Asking Price
$17,000
TTM Revenue
$0
TTM Profit
$0
Last month revenue
$0
Business Details
- Date founded
- 2025-04-01
- Team Size
- 1
- Contact Email
- [email protected]
- Tech Stack
- Wasp, React, Shadcn-UI + TailwindCSS, Prisma + Postgres, hosted on fly.io
✨ More Premium
View all
what your calendar should be

Uptime monitoring, status pages and on-call scheduling in one tool

Unlimited 360° virtual tours: Self-hosted or Cloud.
Fast and secure file uploads with FileFast

Pass the Ontario real estate exam with 4,700+ AI questions

Get exposure with a banner and 30-day placement on all tool pages.
