Ubserve Logo

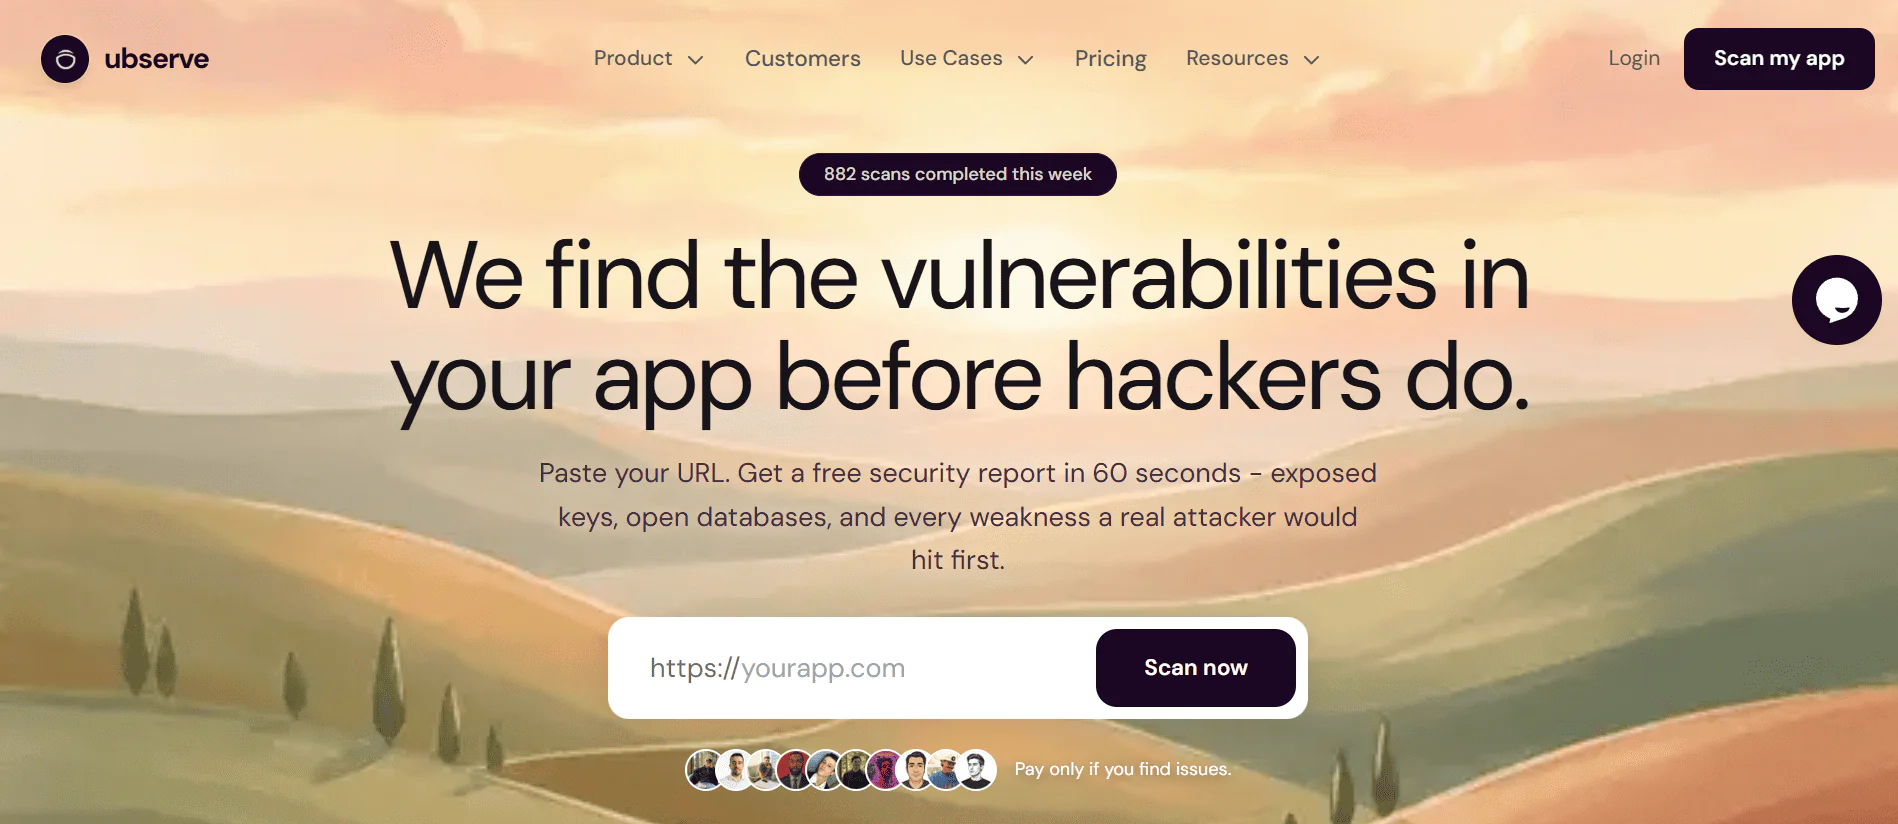
Paste your url and find all the security issues in your app

Screenshot 1 of Ubserve Screenshot 2 of Ubserve Screenshot 3 of Ubserve Screenshot 4 of Ubserve

A placing, not a percentage: #2 of the 20 tools that launched that week. First place reads 90, last reads 35, and the scores compare only within one week.

Judged 19 October 2026 under measure 2026-09-08.v25. Scores compare products within one launch week. We keep making the judges' questions stricter, so a score from another week was set against a different measure.

Market signal

Demand proven, distinction limited

Demand is visible; product differentiation is the main constraint. The research snapshot found 7 direct and 1 adjacent alternatives.

Existing Jury ratings
Demand Mercury
81
Differentiation Uranus
67
Product strength Execution, UX, Trust & Practical value
75
Market scope Market scope unclear

No reliable geographic or language constraint was visible in the public product information.

Similar tools found

7 direct · 1 adjacent

8
Active market Unclear Moderate comparison
Scope unclear 7 Narrower market 1

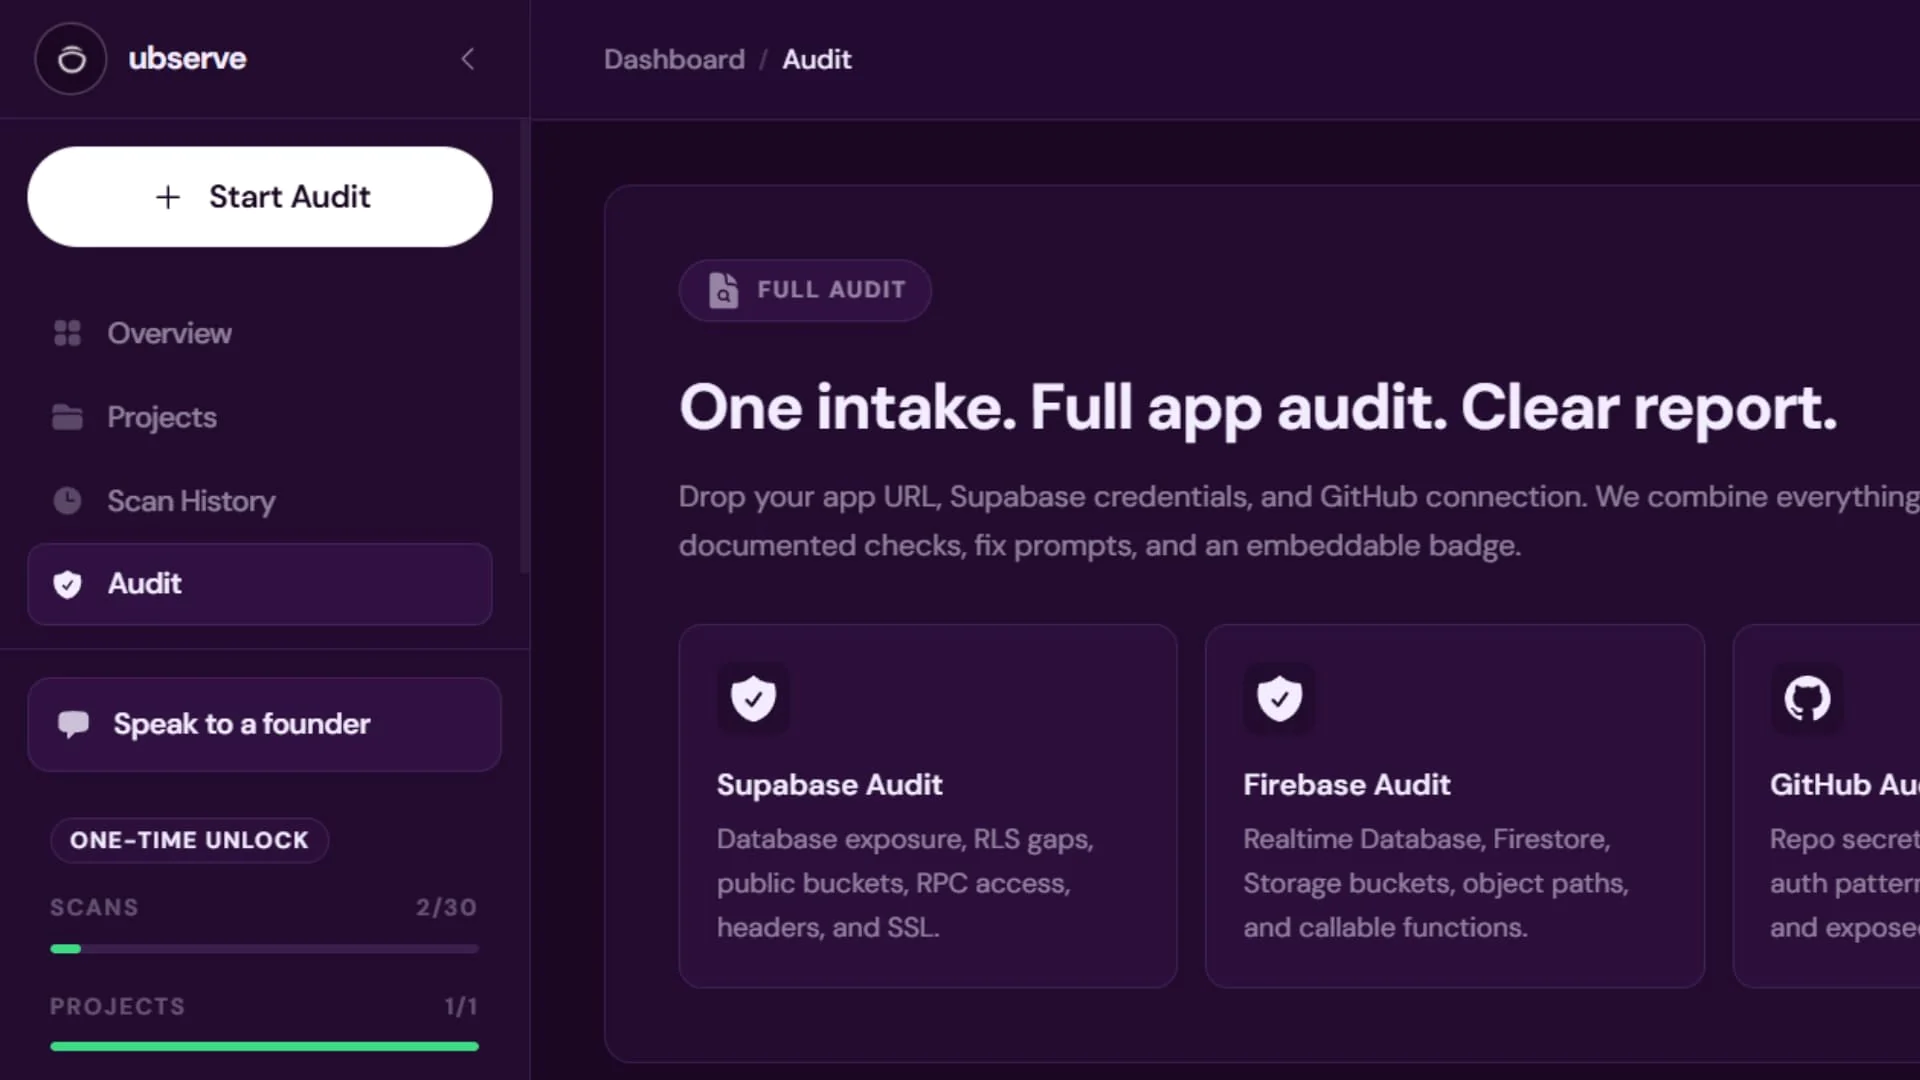
Visible approaches: automated web app testing, IAST.

Examples: AppScan, AppSpider, Aptori, Arachni

Named alternatives found in this public research snapshot, not a complete market census. The count and approach mix explain the review and add no points.

Research coverage Solid coverage
75

The snapshot is useful, with some evidence gaps still visible.

Demand 6 Alternatives 3 Adoption 4

Specialist score profile

All six ratings
Demand 81 Uniqueness 67 Execution 73 UX 87 Trust 61 Value 81

Each spoke is one independent specialist. A smaller side makes the main constraint visible immediately.

This report explains the published specialist ratings and 13 public sources across 13 platforms. Research coverage is not an extra score and adds no points.

Execution

Mars specialist · 15%

#7 of 20 73/100

P18 ranks here because both the homepage and scan page show a real URL input and scan controls for app security checks. It beats P8 on tighter alignment between promise and visible scanner flow, though neither shows a completed result. Total 4/5.

  • P18 ranks here because both the homepage and scan page show a real URL input and scan controls for app security checks. It beats P8 on tighter alignment between promise and visible... Product page

User experience

Venus specialist · 10%

#2 of 20 87/100

Second at 4/5: the first screen includes the actual scanner input and a specific action, but it is one step less direct than P1 because visitors must paste a URL rather than act on a richer in-page workspace.

  • Second at 4/5: the first screen includes the actual scanner input and a specific action, but it is one step less direct than P1 because visitors must paste a URL rather than act on... Product page

Trust

Saturn specialist · 10%

#11 of 20 61/100

It ranks above P1 because the scan claim is narrower and the reachable scan page supports a surface-level security check, but broad security assurances and customer-logo trust cues remain only lightly substantiated.

  • Largest claim is finding security issues in a vibe-coded app by scanning a URL; scan page supports a URL-based app-surface scan in under 60 seconds. Product page
  • Landing page mentions exposed keys, auth, and RLS issues, but the reachable scan page emphasizes JavaScript bundles, headers, secrets, SSL, and HTTPS behavior, suggesting narrower... Product page

Uniqueness

Uranus specialist · 30%

#9 of 20 67/100

Total 2.0. The named difference I could identify is scanning specifically for vibe-coded app issues like exposed keys, broken auth, and missing RLS from a pasted URL. That audience framing is narrower than generic DAST, but the mechanism looks familiar.

  • The product scans a URL for security risks in a vibecoded app, including exposed keys, broken auth, and missing RLS. Product page
  • OWASP lists many general web application scanning tools, indicating the baseline mechanism is established DAST-style scanning. community.owasp.org
  • Typical DAST tools focus on common web vulnerabilities like XSS and SQL injection; the product’s visible emphasis on auth, secrets, and RLS targets a narrower app-building cohort. pentest-tools.com Product page

Practical value

Jupiter specialist · 10%

#4 of 20 81/100

Total 4.0. It produces a named security report after only pasting a URL, and the scan page promises completion in under 60 seconds. It sits below P1 because export/leaving-page evidence is absent and deeper work may still follow elsewhere.

  • Landing page says paste your app URL, we scan your app, and you get your security report. Product page
  • Scan page says 'Scan your app surface in less than 60 seconds' and asks only for app URL. Product page
  • Page says the free scan checks public app surface and catches exposed keys, headers, auth pages, and API endpoints. Product page

Market demand

Mercury specialist · 25%

#4 of 20 81/100

Monthly band: scanning live web apps for vulnerabilities is a real recurring security job for teams shipping software. Total 4.0/5; above P8 because external evidence for web-app scanning is stronger and the need survives any current AI trend.

  • Job is scanning a deployed web app for exposed keys, auth flaws, and other vulnerabilities; typical cadence is monthly or before releases, though exact frequency varies. Product page
  • OWASP lists many application scanning tools, and DAST sources describe automated web vulnerability scanning as an established practice. community.owasp.org github.com
  • Independent comparisons note ZAP and Burp are widely used for automated and manual web application security testing. reintech.io softwaresecured.com

Every specialist function rates every launch. A weekly category leader label marks the highest score in that measure, can be shared on an exact tie, and adds no extra points.

Public research trail

13 relevant sources across 13 platforms. Every link used by the report remains inspectable.

How weekly voting works

Active Deal!

20.00% Off!

Use code: SAVE20 at checkout.

Asking Price

$17,000

Contact Seller

TTM Revenue

$0

TTM Profit

$0

Last month revenue

$0

Business Details

Date founded
2025-04-01
Team Size
1
Contact Email
[email protected]
Tech Stack
Wasp, React, Shadcn-UI + TailwindCSS, Prisma + Postgres, hosted on fly.io